Critical PHP flaw: two vulnerabilities force several European governments to take public websites offline
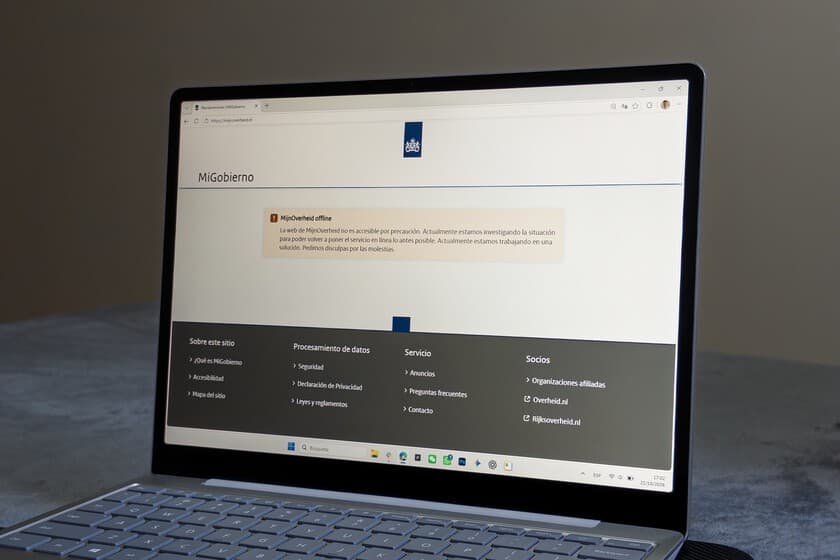
PHP released fixes for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, affecting how the language handles memory errors during a request and potentially allowing remote code execution without prior authentication. Cybersecurity authorities recommend updating immediately and, if that is not possible, taking systems offline. Administrations in the Netherlands, Finland, Denmark and France have temporarily withdrawn websites and public services. Cloudflare reports attack traffic targeting exposed customers.
In 35 seconds
- PHP fixed two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, in the 8.2, 8.3, 8.4 and 8.5 branches.
- The flaws affect memory error handling and could allow remote code execution without logging in.
- Agencies in the Netherlands, Finland, Denmark and France temporarily withdrew websites and public services.
Read the full story at Xataka
IASummary generated by artificial intelligence from a story by Xataka. It may contain errors: the original source prevails.




Comments
Be respectful. Comments reported by several people are hidden until a moderator reviews them.
You do not need an account to read, only to comment. Sign in with a code sent to your email or with your Google account. We only show the name you choose, never your email.