Movistar and Orange clarify what to do if you have a router affected by the Broadcom security flaw
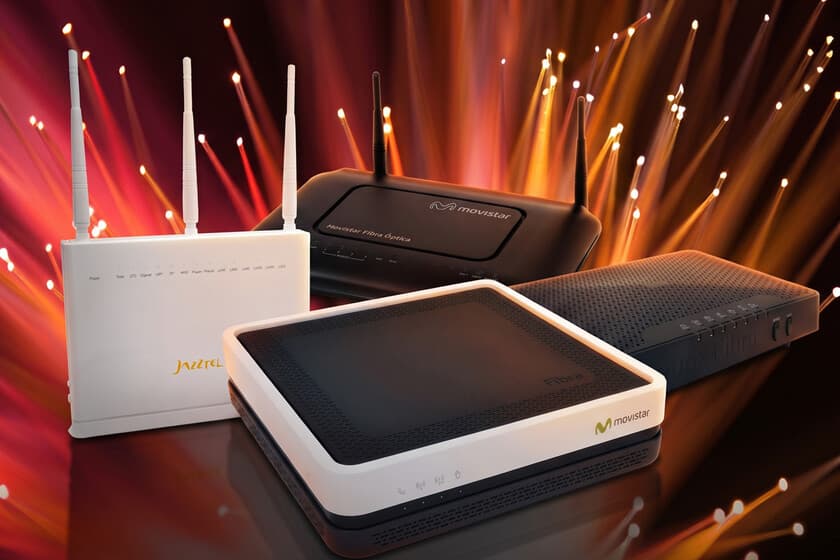
Researcher Quentin Kaiser found, with the help of a cybersecurity-focused AI model, a vulnerability in the firmware of a Broadcom WiFi chip present in home routers from several operators. The flaw allows root access and copying the WiFi network key from RAM remotely and without authentication. Movistar and Orange confirmed to Xataka that they are already working on protective measures and that no device has been compromised to date.
In 45 seconds
- The vulnerability is in the firmware of a Broadcom WiFi chip and allows root access and copying the WiFi key remotely without authentication
- It affects devices with Broadcom chipsets since 2010, including HGU routers from Movistar and O2, Livebox from Orange, Jazztel and Simyo, and Comtrend and ZTE models
- Orange is already rolling out automatic updates and Telefónica is running tests with its suppliers; customers should not change router settings or replace the device
Read the full story at Xataka
IASummary generated by artificial intelligence from a story by Xataka. It may contain errors: the original source prevails.




Comments
Be respectful. Comments reported by several people are hidden until a moderator reviews them.
You do not need an account to read, only to comment. Sign in with a code sent to your email or with your Google account. We only show the name you choose, never your email.