Attackers exploit OpenSSH SSHole flaw hours after disclosure and gain root on a honeypot
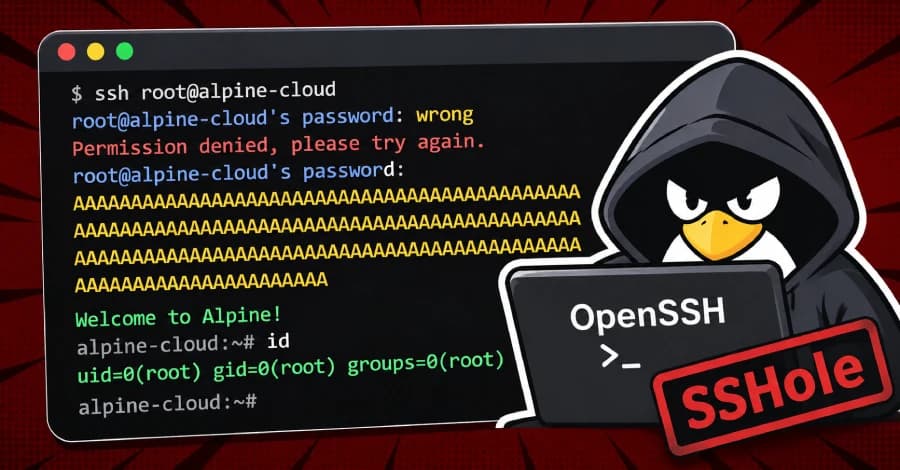
Researchers report exploitation attempts against CVE-2026-123158, known as SSHole, an OpenSSH flaw with a CVSS score of 8.1 affecting Linux systems running OpenSSH on the musl C library with PAM disabled, including Alpine Linux's default configuration. An unauthenticated attacker can supply a password between 257 and 1,024 bytes to access accounts without a usable password. Previdian observed the first attempt less than nine hours after the CVE publication and confirmed root access on an Alpine Linux honeypot. OpenSSH 10.6p2 fixes the flaw.
In 40 seconds
- The CVE-2026-123158 vulnerability, called SSHole, has a CVSS score of 8.1 and affects OpenSSH on musl with PAM disabled, such as Alpine Linux.
- The first exploitation attempt was recorded less than nine hours after the CVE was published, according to Previdian.
- Previdian confirmed root access on an Alpine Linux honeypot and eight attempts from an IP geolocated in Japan.
Read the full story at The Hacker News
IASummary generated by artificial intelligence from a story by The Hacker News. It may contain errors: the original source prevails.


Comments
Be respectful. Comments reported by several people are hidden until a moderator reviews them.
You do not need an account to read, only to comment. Sign in with a code sent to your email or with your Google account. We only show the name you choose, never your email.